
The post has been translated automatically. Original language: Russian




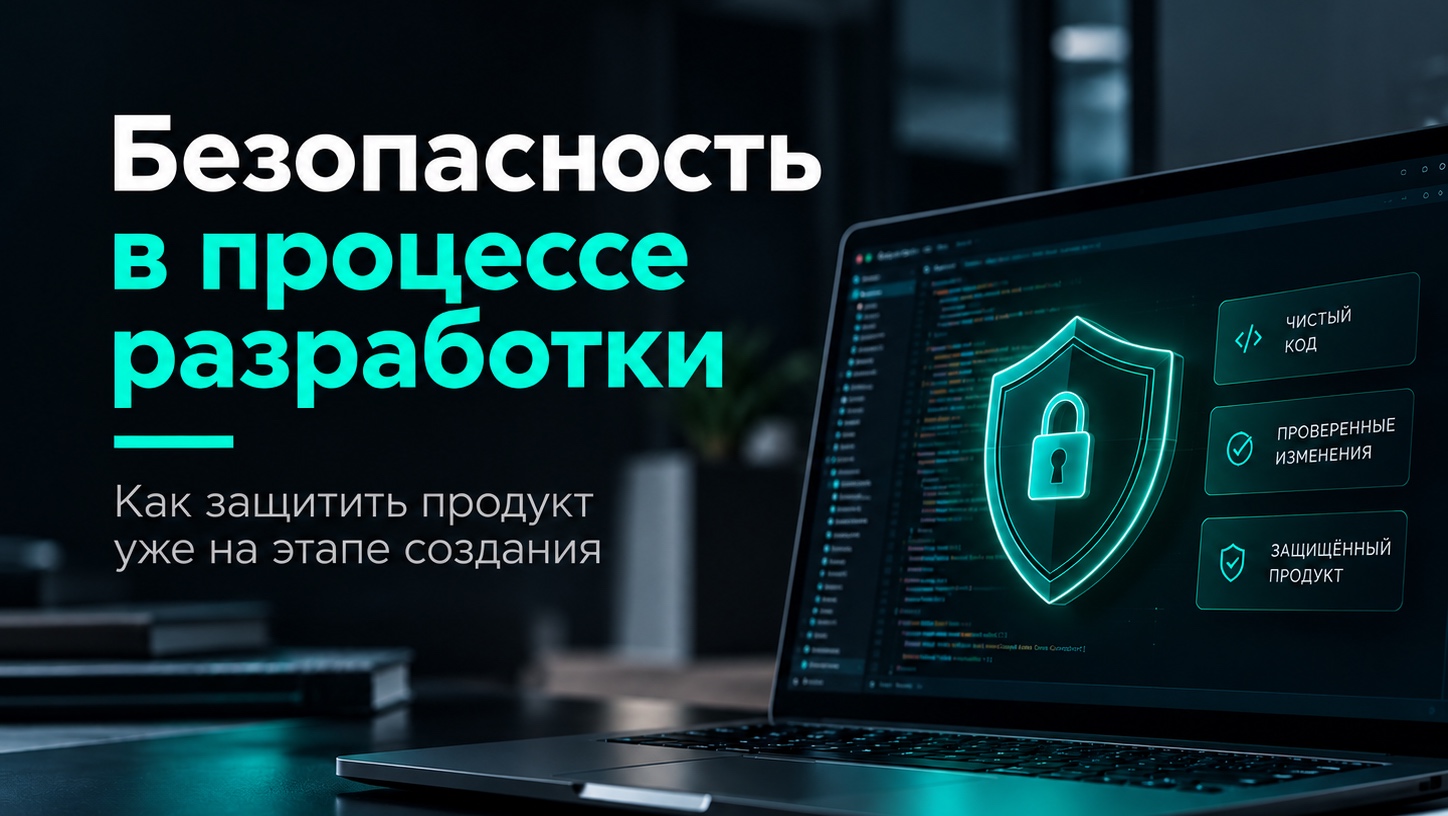
Security in the development process: what is important to monitor?
The safety of a product does not begin after its launch, but already at the development stage. The sooner vulnerabilities and errors are identified, the fewer risks arise in the following stages.
There are several key elements of secure development.
1. Code control
The code is the first line of defense. During the development process, it is important to regularly check it for vulnerabilities, verify changes before merging, and protect major versions of the code from direct changes.
2. Automation of inspections
Some of the security checks can be automated and integrated directly into the development process.:
- vulnerability analysis of the code;
- checking third-party components and libraries;
- Search for randomly published passwords, keys, and other secret data;
- stop the build when critical risks are detected.
3. Change control
It is important to understand who made the changes to the code, when, and what. For this, the revision history, authorship confirmation, and repository protection are used.
This approach allows you to make security a part of the entire development process, rather than a separate check before the release of a product.
Safety must be built into the product from the very beginning.
Безопасность в процессе разработки: что важно контролировать?
Безопасность продукта начинается не после его запуска, а уже на этапе разработки. Чем раньше выявляются уязвимости и ошибки, тем меньше рисков возникает на следующих этапах.
Есть несколько ключевых элементов безопасной разработки.
1. Контроль кода
Код - первая линия защиты. В процессе разработки важно регулярно проверять его на уязвимости, проводить проверку изменений перед объединением и защищать основные версии кода от прямого внесения изменений.
2. Автоматизация проверок
Часть проверок безопасности можно автоматизировать и встроить непосредственно в процесс разработки:
- анализ кода на уязвимости;
- проверка сторонних компонентов и библиотек;
- поиск случайно опубликованных паролей, ключей и других секретных данных;
- остановка сборки при обнаружении критических рисков.
3. Контроль изменений
Важно понимать, кто, когда и какие изменения внёс в код. Для этого используются история изменений, подтверждение авторства и защита репозитория.
Такой подход позволяет сделать безопасность частью всего процесса разработки, а не отдельной проверкой перед выпуском продукта.
Безопасность должна закладываться в продукт с самого начала.
 Share